
A customer or partner sent you a security questionnaire you can’t answer.
We review the code and fix the gaps.
We check your application against the OWASP Top 10, fix what we find and give you plain answers about how data is stored and protected.
We are a development team that takes security seriously, not a penetration-testing firm. Every build follows the OWASP Top 10, encrypts sensitive data and includes two-factor login. We also review and fix code other teams wrote.
The security questions we get most.
A customer or partner sent you a security questionnaire you can’t answer.
We check your application against the OWASP Top 10, fix what we find and give you plain answers about how data is stored and protected.
Your app holds health, children’s or financial data and you’re not sure it is handled properly.
COMPASS and Rezi24 follow HIPAA and GDPR-style data handling, and E2P+SEND held records for 352 UK schools. We apply the client’s guidelines to how records are stored and kept.
Your app was built quickly, maybe with AI tools, and nobody has checked it.
AI-built apps often ship with exposed keys, missing permission checks or no rate limits. We find and fix those first.
You need a certified penetration test.
We don’t do offensive testing and hold no certifications. We can fix what a pen-test firm finds, and we’ll point you to one if you need a formal report.
Defensive, practical security for the software you build or run.
OWASP Top 10 practice on every project: input validation, safe queries, permission checks on every action and secrets kept out of the code.
We review code another team or an AI tool wrote, list the problems in plain English and fix them.
Two-factor login, roles and permissions, and session handling done properly.
Sensitive data encrypted in storage and in transit, with keys kept out of the application code.
Storing, keeping and deleting records according to the rules your client or regulator sets.
COMPASS, Rezi24 and i-mve.
Health, children’s and personal records. We say plainly which clients we still work with.
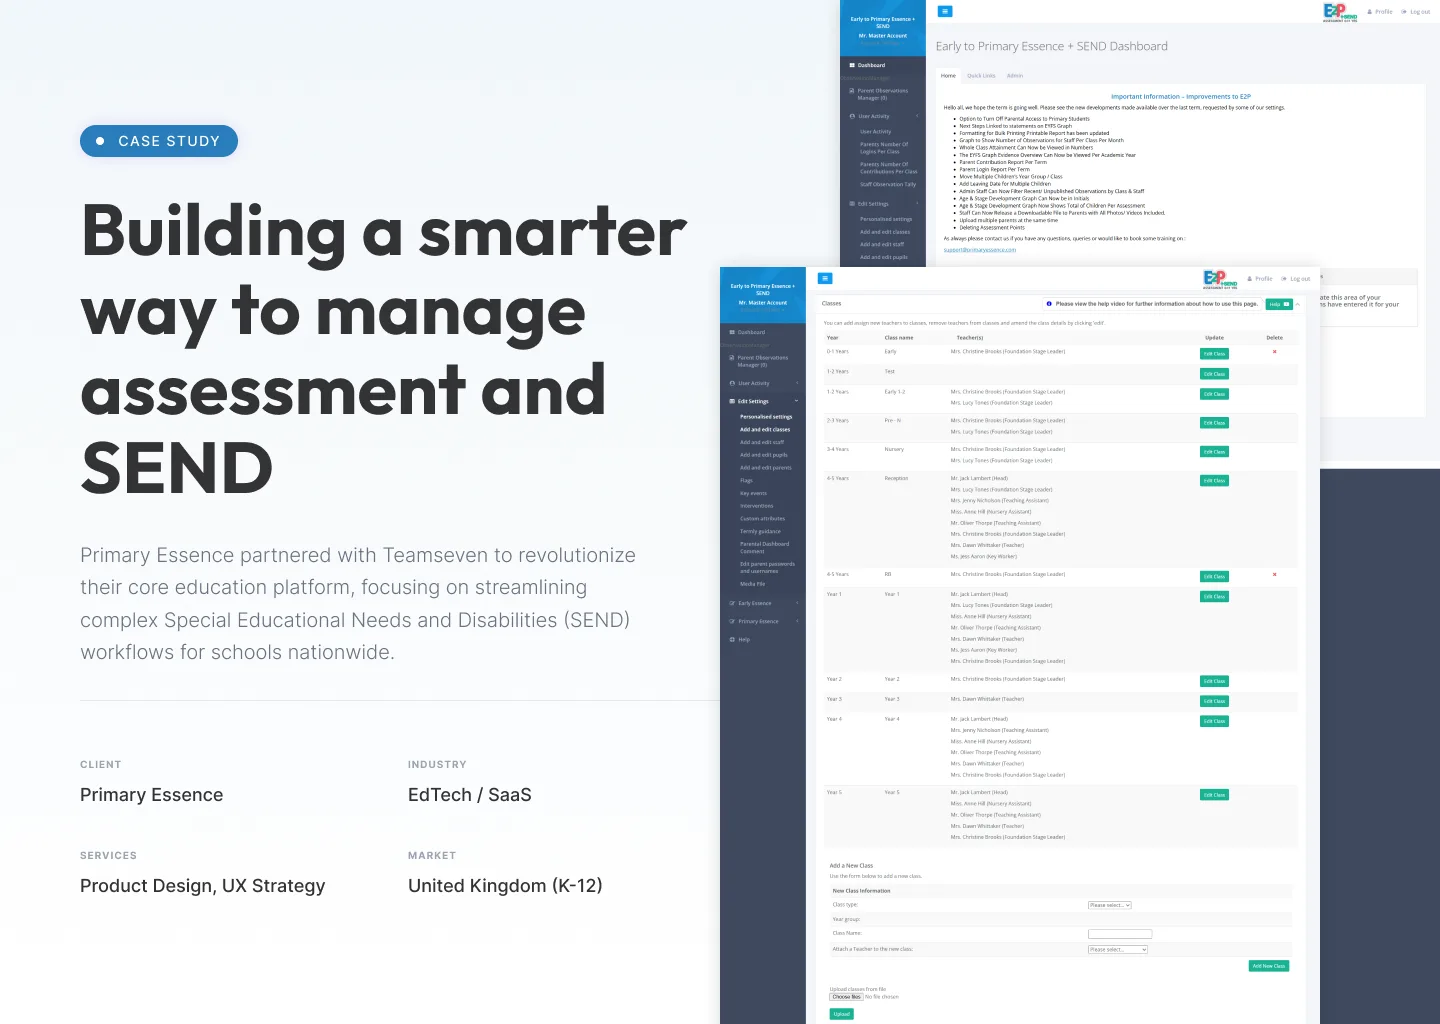
Schools track what each child learns from early years through primary, with observations, photos and SEND records that staff and parents can both see.
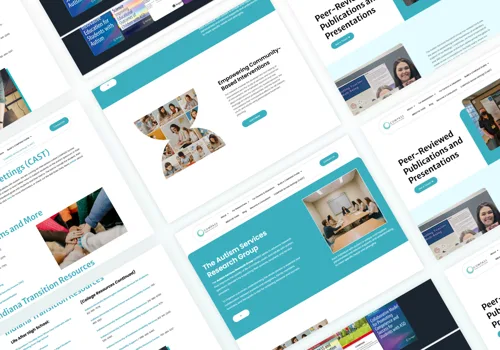
A platform for a PhD-led autism programme. Trainers, consultants, teachers and parents follow each child’s plan through surveys, consultations and coaching over a year.
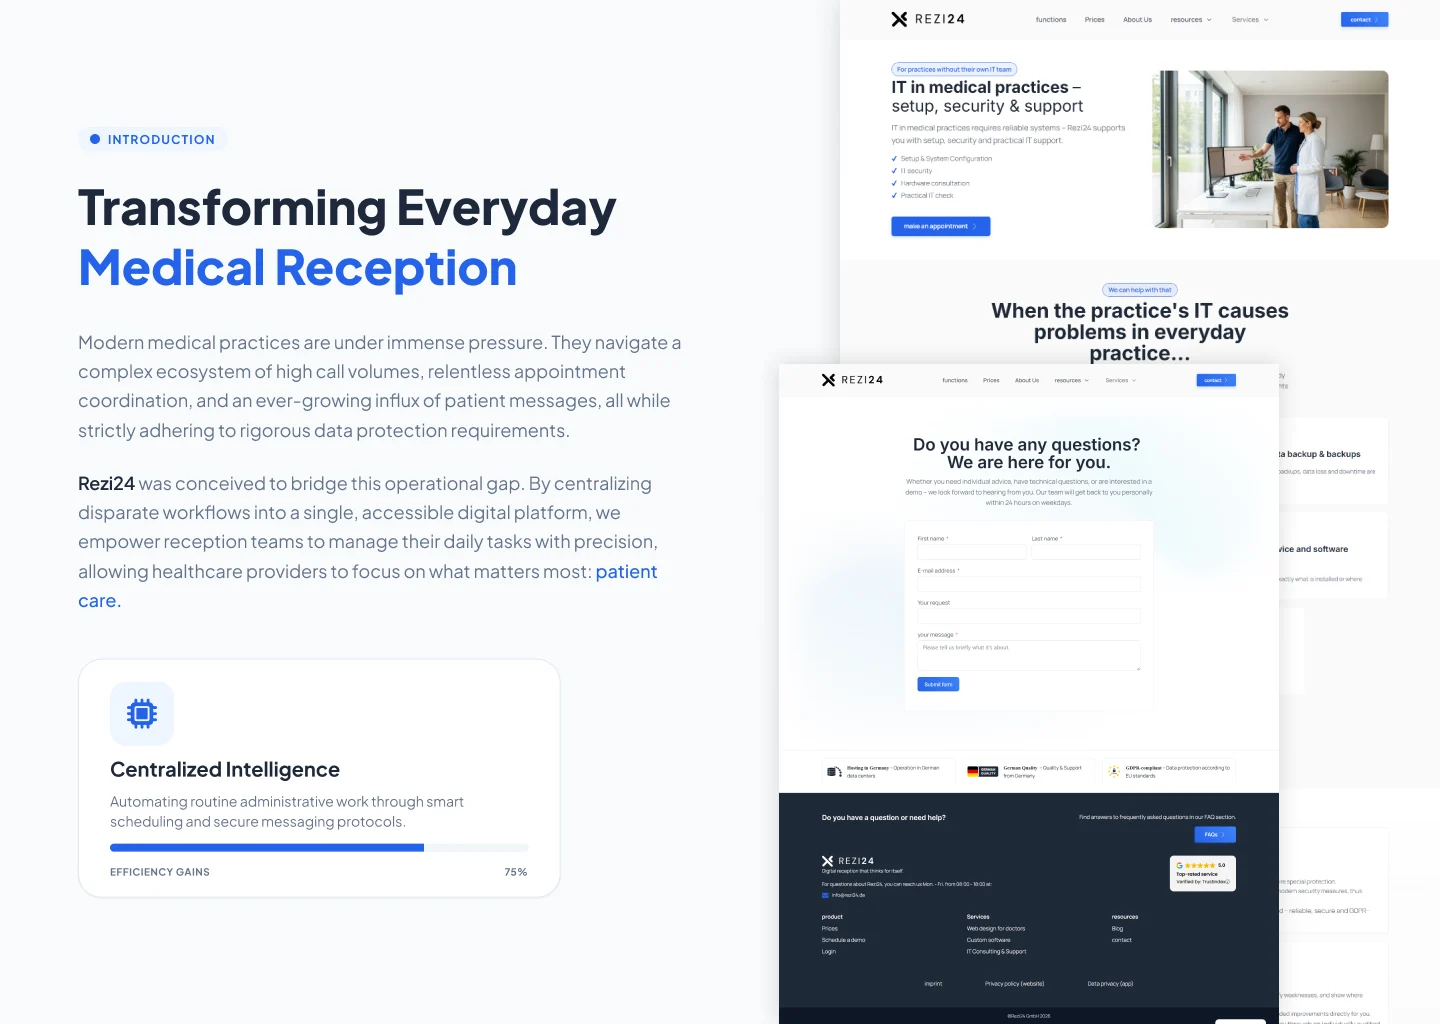
An online reception for German medical practices: patients book appointments at any hour and reception staff take fewer calls.
For new builds, security is part of every step. For existing code, it starts with a review.
Tell us what the system does, what data it holds and who is asking questions about it.
Read access to the repository and a written quote for the review and likely fixes.
We check authentication, permissions, input handling, secrets, dependencies and how sensitive data is stored.
Each problem, how serious it is and what fixing it involves, ordered by risk.
Fixes go through your normal review process, with updates twice a week on Slack.
Optional maintenance keeps dependencies and security patches up to date.
It depends on scope, so we do not publish a price list. Every project is a fixed quote, in writing, after a 30-minute call.
Security is not a one-off. Optional maintenance keeps dependencies and patches current.
Platform-level reviews of the agency, not cherry-picked project comments.
What I love about Team7 is that they always say: No worries, we can find a solution. This is the mindset of builders, creators, people who do not have fear, the partner you need if you want to excel.
Working with Mo and his team over the past year has been nothing short of exceptional. I was admittedly sceptical about investing such a large amount, but results exceeded every expectation.
Their responsiveness and willingness to take on our challenging task were impressive.
They are amazing and consistently exceed expectations. They go above and beyond what is asked of them and their communication is top notch, so much so that we joke that they never sleep. The best of the best.
Straight answers on what we do and don’t do.
Ask us something elseNo. We are a development team that writes and reviews code for security. We don’t do offensive testing. If you need a formal pen-test report, use a specialist firm, and we can fix what they find.
No, we hold no security certifications. What we do is follow the OWASP Top 10 on every build, encrypt sensitive data and include two-factor login as standard.
Yes. COMPASS and Rezi24 were built to HIPAA and GDPR-style data-handling rules, and i-mve and others follow GDPR. In practice that means following the client’s guidelines for how records are stored, accessed, kept and deleted.
Yes. Most reviews are of code we didn’t write, including apps built with AI tools. You get a plain-English list of findings ordered by risk, and a quote to fix them.
You do. At handover you get the Git repositories and written documentation. There is nothing tying the software back to us, so you can take it to an in-house team whenever you like.
Rehan, one of our two founders, is your day-to-day contact. You get updates on Slack twice a week and can see the code in your repository at any time. We split working hours between us to cover US, UK and Australian time zones, and we usually reply within an hour, sometimes the next morning.
A 30-minute call. Tell us what the system holds and who is asking. We’ll tell you what a review involves and what it costs.