
What a Code Audit Should Tell You, and What It Should Cost
A good code audit answers plain business questions: is it safe, will it hold up, what will it cost to fix?
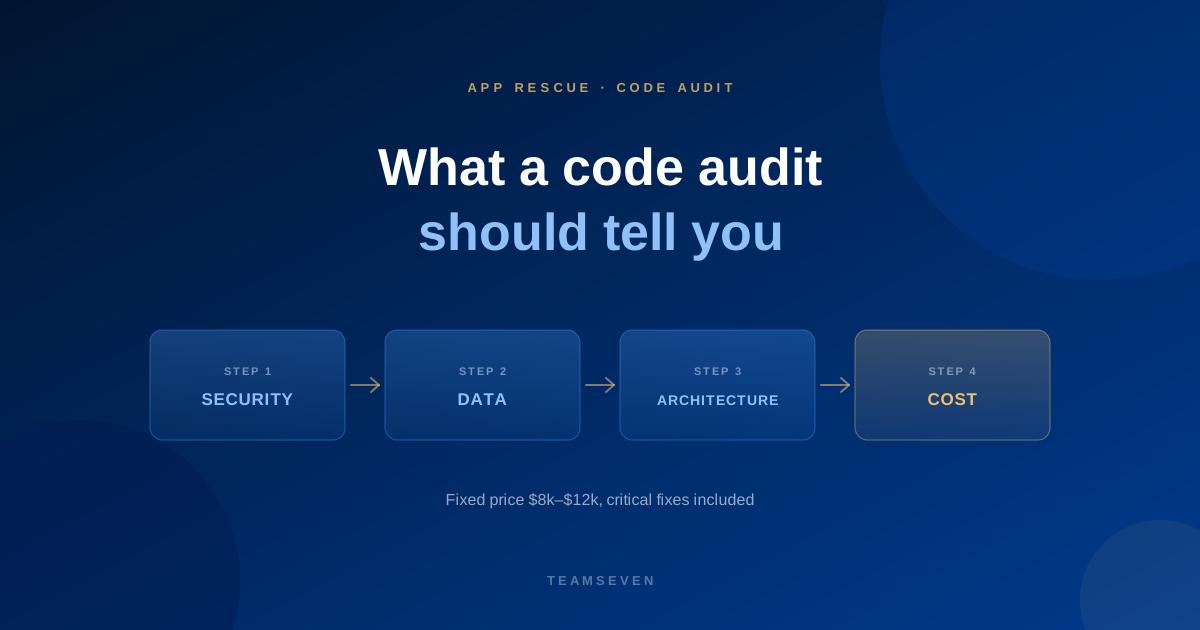
Most founders ask for a code audit for one of three reasons: they inherited an app, an AI tool built it, or someone is about to invest in it or buy it. In each case the real questions aren't technical. They're business questions:
- Is it safe to put real customers on it?
- Will it hold up as we grow?
- What will it cost to fix, and what can wait?
- Do we need to rebuild it?
A useful audit answers those in plain English. A poor one hands you two hundred warnings from an automated tool and leaves you to work out what matters.
What a good audit covers
Security
Logins, permissions, data exposure and secrets in the code, checked against the OWASP Top 10. For AI-built apps, the same five holes come up again and again.
Data
Is the data model going to hold real customers? Is personal data protected? Are there backups, and has anyone ever restored one? If the app runs on Supabase, are the row-level security rules right?
Architecture
How the pieces fit together, what depends on what, and which parts will be painful to change. This is where you learn whether new features will be cheap or expensive.
Performance
Slow pages and slow queries, found and measured, not guessed.
Hosting and costs
Where it runs, what it costs, what happens if it goes down, and who holds the accounts.
What the report should look like
- A summary for the founder or investor, in plain language
- Findings ranked by urgency: fix now, fix soon, fine for now
- A rough cost to fix each group
- A clear recommendation: keep and fix, refactor, or rebuild parts
- Technical detail in an appendix for whoever does the work
And a walkthrough call, because a report nobody discusses rarely gets acted on.
What an audit isn't
A code audit reviews the code and configuration. It isn't a formal penetration test, and it doesn't come with a security certificate. We say so plainly; if an investor needs a certified penetration test, that's a separate specialist engagement.
What it costs
Prices vary widely. Ours is a fixed $8,000–$12,000, which includes the review, the written report, a walkthrough call and fixes to the critical security and stability issues. Where you land in that range depends on the size of the app. Everything beyond the critical fixes is quoted separately, and only if you want us to do it. The report is yours either way.
See our code audit service for the full scope.
How long does a code audit take?
It depends on the size of the app. The review itself is usually measured in days to a couple of weeks, followed by the critical fixes. You'll get a timeline with the fixed price.
Do I have to hire the same team to fix the problems?
No. A good report is written so any competent team can act on it. We're happy to quote for the remaining work, but you're free to take the report elsewhere.
When should I get a code audit?
Before you put real customers on an app you didn't build, before you raise money or sell, and whenever a developer leaves. If your developer has already gone, start with the first 72 hours.
Stay connected
Build notes, launches, and new articles from the Teamseven team.